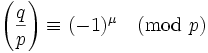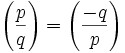Friday, February 03, 2006

Groups and Abelian Groups

Group theory is one of the most fundamental and important ideas in all of mathematics. The basic insight came out the theory of algebraic equations (which I will explore in more detail in a future blog)

Evariste Galois first defined the concept of a group in 1832. It took a long time before people generally appreciated the importance of the idea. The mathematical community eventually recognized its importance when Louisville presented a reedited version of Galois's papers in 1846.

At the time Galois and Abel enter the picture, it was well known that there exists an equation for solving the quadratic equation (ax2 + bx + c=0), the cubic equation (ax3 + bx2 + cx + d = 0), and the quartic equation (ax4 + bx3 + cx2 + dx + e=0). It was suspected that no such equation existed for the quintic equation (ax5 + bx4 + cx3 + dx2 + ex + f=0)

Niels Abel was the first to prove that there was no general solution for the quintic equation. His proof is one of the highpoints of mathematical theory and made use of what are today called abelian groups.

Evariste Galois submitted a paper on the solution to the quintic equation as an entry to the Paris Academy's Grand Prize in 1829. The story goes that his entry was returned by Cauchy because it had been predated by Abel's solution which was entered posthumously for the Grand Prize. Galois then generalized his paper to cover all equations quintic or higher. Due to the death of his reviewer, Galois's rewritten paper was never considered and the Grand Prize of 1830 was awarded to Abel and Jacobi.

Galois's proof is one of the most important insights in all of mathematics. He showed that proper understanding of an algebraic equation as a group of permutations determines whether an algebraic equation is solveable through a general algebraic equation. To accomplish this, Galois made use of permutations and what is today known as field theory. I will talk about these other ideas in a future blog. For now, I will focus on groups and abelian groups.

Before defining a group, we need to define four concepts: closure, associativity, identity element, inverse, commutativity.

Definition 1: Closure: When the operation is applied to any two elements of the set, the result is also an element of the set.

This is true of multiplication with integers (an integer * an integer = an integer) and multiplication with fractions ( a fraction * a fraction = a fraction).

It is not true of division with integers (many integer divisions result in a fraction) and it is not true of fractions (consider division by 0 which has an undefined result)

Definition 2: Associativity: if we have three elements, a,b,c, then the (ab)c = a(bc).

This is true of multiplication and addition with integers.

It is not true of subtraction with integers (5 - 6)-1 ≠ 5 - (6-1)

It is also not true of division since (1 / 2) / 2 ≠ 1 / (2/2)

Definition 3: Identity Element: there exists an element such that all elements applied to this element result in the original element.

This is true of addition and multiplication where 0 is the identity element in addition and 1 is the identity element in multiplication.

Definition 4: Inverse: there exists an element that when multiplied with a given element results in the identity element.

This is true of multiplication with nonzero rational numbers. 5 * (1/5) = 1

This is true of multiplication of nonzero real numbers. (1/3) * 3 = 1

This is not true of multiplication with integers. For example, there is no whole number integer x such that 2x = 1.

Definition 5: Commutativity: for any two elements, the operation has the same value regardless of the order, that is, ab=ba.

This is true of multiplication and addition:
1 + 3 = 3 + 1
2 * 3 = 3 * 2

This is not true of subtraction or division.
1 - 3 ≠ 3 - 1
1 / 3 ≠ 3 / 1

Now, we can define a group and an abelian group.

Definition 6: Group: A group is defined as a set of elements and a mathematical operation such that:
(a) Closure: For any two elements of the group, the mathematical operation results in an element of the group.

(b) Associativity: For any three elements of the group, (ab)c =a(bc).

(c) Identity Element: There exists an element i that when combined with any element a, we get: ai=a

(d) Inverse Element: For any element a in the group, there exists an element b also in the group such that ab = i (the inverse element).

Example 1: Addition on integers forms a group.

(a) Closure: integer + integer = integer

(b) Associativity: for all integers (a + b) + c = a + (b + c)

(c) Identity Element: 0: for all integers (a + 0) = a

(d) Inverse Element: For all integers a, a + (-a) = 0

Example 2: Multiplication on integers is not a group.

(a) Closure: integer * integer = integer (true)

(b) Associativity: for all integers (a * b) * c = a * (b * c) ( true)

(c) Identity Element: 1: for all integers a * 1 = a (true)

(d) Inverse Element: 2 does not have an inverse element. (false)

Example 3: Multiplication on nonzero rational numbers is a group.

(a) Closure: rational number * rational number = rational number

(b) Associativity: for all rational numbers (a * b) * c = a * (b * c)

(c) Identity Element: 1: for all rational integers: a * 1 = a

(d) Inverse Element: for any rational number a/b, there exists b/a such that (a/b)(b/a) = 1

Definition 7: Abelian Group: An abelian group is a group that also has the property of being commutative.

Example 1: the addition of integers is an abelian group.

(a) See Example 1 above to see why it is a group.

(b) Commutative: a + b = b + a

Theorem: For a given odd prime p, the multiplication of units modulo p form an abelian group.

NOTE: If you are not familiar with units modulo p, review here.

(1) Closure:

(a) Let a,b be units modulo p.

(b) By definition (see here), there exists a',b' such that (a)(a') = 1 (mod p), (b)(b') = 1 (mod p).

(c) So (a)(a')(b)(b') ≡ 1 * 1 ≡ 1 (mod p)

(d) (a)(b)(a')(b') = (a)(a')(b)(b') [Since integers are commutative]

(e) (ab)(a'b') ≡ 1 (mod p) so by definition (ab) is a unit modulo p.

(2) Associativity:

(a) Let a,b,c be units modulo p.

(b) a(bc) = (ab)c [Since integers are associative]

(c) So a(bc) ≡ (ab)c (mod p).

(3) Identity Element:

We know that 1 is a unit modulo an odd prime p.

(4) Inverse:

This is true by definition of units modulo p (see here).

(5) Commutativity:

(a) Let a,b be units modulo p.

(b) ab = bc [Since commutativity of integers with multiplication]

(c) So (ab) ≡ (bc) (mod p)

QED

References

Wednesday, February 01, 2006

Èvariste Galois

Èvariste Galois was born on October 25, 1811 in La Reine, France. Galois was educated by his mother up until he was 12. There was some discussion about sending him to college when he was 10 but in the end, it was decided that he should stay at home. In 1815, his father was elected mayor of La Reine.

In 1823, enrolled in school. In 1824-1825, he received good grades, but in 1826, he was forced to repeat a grade because he failed rhetoric. In 1827, Galois enrolled in his first math class.

In 1828, just one year after his first math class, Galois took the entrance examination for the Ecole Polytechnique, the top university. He failed.

Despite the setback, Galois continued his studies of mathematics including work by Lagrange and Legendre. In April 0f 1829, he published a paper on continued fractions which included the proof that reduced quadratic equations are represented by purely periodic continued fractions.

Later that year, a scandal erupted when a vulgar poems were distributed and attributed to Galois's father. The result was more than Galois's father could stand and he committed suicide on July 2, 1829. Just a few weeks later, Galois made his second attempt at entrance to the Ecole Polytechnique. Again, he failed. In December of 1829, Galois entered Ecole Normale.

Galois submitted a paper on the theory of equations to be published. He learned that the same topic had just been covered in a posthumous article written by Niels Henrik Abel. Galois rewrote the article on the conditions whereby an equation is soluble by radicals and resubmitted it. The paper was ver well received and was submitted to Fourier who was secretary of the Paris Academy for the Grand Prize. Unfortunately, Fourier died in April of 1830 and Galois's paper got lost. In June, the Grand Prize of the Paris Academy was awarded to Niels Henrik Abel and Carl Jacobi.

In July of 1830, there was revolution in France. Charles X quickly departed and riots broke out. The head of the Ecole Normale locked the students in a the school to prevent them from joining in the unrest. In 1830, the director of the Ecole Normale wrote an editorial criticizing the students for their behavior. Galois wrote a response defending the students and criticizing the decision to do a student lock up. After writing this reply, Galois was expelled.

Galois next entered the Artillery of the National Guard. In December of 1830, King Louis Philippe disassembled the Artillery of the National Guard because he saw them as a threat to his power. 19 of the guards had been accused of conspiracy but were later released. On May 9, 1831, a great celebration was put together. Galois was there. At one point, Galois raised his glass to make a toast and held up a dagger at the same time. This was taken as a threat against the king. That same evening, Galois was arrested. He was held in prison until June 15 when he was acquitted.

On July 14, Galois was arrested for wearing the uniform of the Artillery of the National Guard which had been outlawed. While in prison, he found out that one of his math papers had been rejected and he attempted suicide. He was stopped by the other prisoners. Finally, on April 29, he was released.

By this time, he was in love with a young woman he had met. On May 30, he entered into a duel. It is believed that it was over the young woman. During the fight, he was severely wounded and died on May 31, 1832 at the age of 20.

Galois's papers were collected and sent out. Eventually, they made their way to Joseph Liouville who was deeply impressed. Liouville presented them to the French Academy in September 1843. These papers were published in 1846 and form the basis of what is today known as Galois Theory.

Today, Galois is considered to be one of the most original and talented mathematicians of all time and Galois Theory is one of the great gems of modern mathematics.

References

Niels Henrik Abel

Niels Henrik Abel was born on August 5, 1802 in Frindoe, Norway. His father was a vicar in the village of Gjerstad. His father was active politically and was part of the movement that led to Norway's separation from Denmark in 1814.

When Niels was 13 years old, he left home to attend the Cathedral School in Christiania. The school was set up in the new ideals of the time. Instead of corporal punishment, in theory, teachers appealed to a student's sense of honor and decency. Unfortunately, these ideals were not deep in practice. The math teacher at the school would have students copy math problems from the chalkboard and then he would discipline any student who did not learn the lesson. In November, 1817, this math teacher beat a student so badly that the student died. After a protests from the students, the teacher was fired.

It was at this time that a new math teacher came to the school: Bernt Michael Homboe. He had a great love for mathematics that went beyond the standard mathematical education of the day in Norway. He assigned students independent projects. He was very impressed by the abilities of young Niels Abel and helped him to study advanced mathematical topics.

Niels began to greatly excel in mathematics. Despite this, many of the school's teachers were distressed by what was perceived as an overfocus on math. At this time, classical languages were considered the paradigm of a solid education. Abel would regularly visit the public library to study the works of Newton, Euler, Gauss, and Lagrange.

At the time, the University of Christiania offered major only in theology, medicine, or law. There was no track for mathematics. For this reason, Abel studied mathematics on his own. It was very clear that in order to continue his studies, he needed to go abroad. Owing mostly to a lack of funds, Abel stayed at the University of Christiania for 4 years.

In 1823, Abel moved to Denmark where he was able to meet the leading Nordic mathematician of the day, Ferdinand Degen. He lived with his aunt and her husband in Christianshavn. In his private studies, he made progress on number theory and elliptic equations. He also met his future fiancee Christine Kemp.

Abel's first proof was about the impossibility of finding a solution to the quintic equation which he published in 1824 when he was 22 years old. He translated the article to French and he condensed the proof to 6 pages. The resulting article was very difficult to read and was largely ignored by the leading mathematicians.

In 1824, he got a government grant to study mathematics abroad for 2 years. It was during these travels that he met an engineer named Leopold Crelle. In 1826, Crelle launched his soon-to-be-famous math magazine, Crelle's Journal. It was here that Abel would publish most of his work.

It was in Crelle's Journal, that Abel published an expanded version of his proof of the impossibility of solving the general quintic equation, a treatise on the binomial series, and six other submissions.

In July of 1826, Abel headed to Paris. His goal was to impress the very well established Paris Academy. He had worked hard to create a treatise on elliptic integrals. Known today as the Paris Treatise, this is a major mathematical breakthrough. In it, he establishes research areas that are still continuing today and he presented a generality of results that went beyond the mathematics of the day. He submitted this treatise to the Paris Academy in October of 1826. He never heard back. By the end of 1826, he headed back to Norway.

Once back, despite a lack of funds, Abel continued to make great advances in mathematics. He submitted a constant barrage of articles to Crelle's which was not able to publish them as quickly as Abel wrote them up.

In the Autumn of 1828, while Abel was making plans for his marriage, he became very sick and died. He was 26. A few weeks after he died, a letter from Crelle arrived offering Abel an important post in Berlin.

In 1841, the Paris Treatise was published in the Paris Academy's Journal.

References

Saturday, January 28, 2006

Quadratic Reciprocity: Gauss's Lemma for Quadratic Residues

In today's blog I continue the proof for the Principle of Quadratic Reciprocity. If you are not familiar with the concepts of quadratic reciprocity, quadratic residues, or the Legendre Symbol start here.

If you would like to start this proof at the beginning, start here.

Today's proof is taken from Gareth A. Jones and J. Mary Jones' Elementary Number Theory.

Definition 1: Congruence Class (mod n)

The set of all numbers that are congruent to each other modulo a value n. This congruence class is represented in brackets such as [0].

NOTE: If you are not familiar with the concept of congruence or modulo, you can review modular arithmetic here.

If we consider n = 3, then we see that:
[1] = { ... ,-2, 1, 4, 7, ... }

since:

-2 ≡ 4 ≡ 7 ≡ 1 (mod 3).

Definition 2: Unit (mod p)

A congruence class [a] is a unit mod p if there exists another congruence class [b] such that ab ≡1 (mod p).

Here are some examples:

1 is a unit mod 8
3 is a unit mod 8 since (3)(3) ≡ 1 (mod 8)
5 is a unit mod 8 since (5)(5) ≡ 1 (mod 8)
7 is a unit mod 8 since (7)(7) ≡ 1 (mod 8)

Lemma 1: Let p be an odd prime. Let P be the set { 1, 2, ... (p-1)/2 }. Let x,y be elements of P.
Then: x ≠ y → x ± y is not congruent to 0.

(1) Assume that x is less than y (otherwise, we can use the same arguments on y)

(2) Case I: x + y

3 ≤ x + y ≤ (p-1)/2 + (p-1)/2 -1 = (p-1)/2 + (p-1-2)/2 = (2p -4)/2 = p-2.

(3) Case II: x-y

-1 ≥ x-y ≥ 1 - (p-1)/2 = (2 - p + 1)/2 = (-p + 3)/2 = -(p-3)/2

(4) Case III: y-x

1 ≤ y - x ≤ (p-1)/2 - 1 = (p-1-2)/2 = (p-3)/2

QED

Lemma 2: Let p be a prime, let a be an integer such that gcd(a,p)=1. Let P be the set { 1, 2, ... (p-1)/2 }. Then:
x ∈ P, y ∈ P, ax ≡ ± ay → x=y

(1) Assume that ax ≡ ± ay (mod p) and x ≠ y.

(2) ax ± ay ≡ 0 (mod p) [See here for a review of modular arithmetic if needed]

(3) So, p divides a(x ± y)

(4) But p doesn't divide a since gcd(a,p) = 1

(5) So, p divides x ± y [By Euclid's Lemma]

(6) So, x ± y ≡ 0 (mod p)

(7) But x ± y is not congruent to 0 (mod p) from Lemma 1 above.

(8) So we have a contradiction and we reject (#1)

QED

Corollary 2.1: If p is an odd prime and P = { 1, 2, ... (p-1)/2 } and gcd(a,p)=1, then there exists εi where aP = { (ε1), (ε2)(2), ... (ε(p-1)/2)[(p-1)/2] } and each εi = +1 or -1.

(1) We know that each element of aP must be in { ±1, ±2, ... ±(p-1)/2 } since:

(a) Let b be any element of P.

(b) We know that ab must fit into one of the following congruence classes [± 1], [± 2], ... [ ±(p-1)/2 ] since ab (mod p) must be between 0 and p-1.

(c) But this means that either it is between 0 and (p-1)/2 or it is between (p-1)/2 + 1 and p - 1.

(d) If it is between 0 and (p-1)/2 then we are done.

(e) If it is between (p-1)/2 + 1 and p-1, then ab (mod p) is between -(p-1)/2 and -1 since p-1 ≡ -1 (mod p) and since [(p-1)/2 + 1] ≡ -(p-1)/2 (Consider that (p-1)/2 + 1 + (p-1)/2 = (p-1+2 +p - 1)/2 = 2p/2 = p.)

(f) But then either way ab is in { ± 1, ± 2, ... ± (p-1)/2 }

(2) We know that aP = { ±1, ±2, ... ±(p-1)/2 } since:

(a) Let's suppose we have b,c such that b,c ∈ P and b ≠ c.

(b) Then, we know that that ab is not congruent to ac from Lemma 2 since it if they were congruent then they must be the same which contradicts our assumption.

QED

Lemma 3: if p is an odd prime and a is a unit mod p, then a(p-1)/2 ≡ (∏εi) (mod p) where εi is derived from aP as in Corollary 2.1 above.

(1) We know that aP = { ± 1, ± 2, ... ±(p-1)/2 } where at each point εi = 1 or -1 [See corollary 2.1]

(2) (∏εi) ≡ [(a*1)(a*2)...(a*(p-1)/2)]/[(1)(2)...(p-1)/2] (mod p)

NOTE: We can make this assumption since multiplication in modular arithmetic is an abelian group. More details here.

(3) Now, be definition of factorial [(p-1)/2]! ≡ (1)(2)...(p-1)/2 [See here for review of factorials]

(4) Likewise (a*1)(a*2)*...*(a*[p-1]/2) ≡ a(p-1)/2[(p-1)/2]! (mod p)

(5) Combining #2 with #3 and #4 gives us:
(∏εi) ≡ a(p-1)/2[(p-1)/2]!/[(p-1)/2]! = a(p-1)/2 (mod p)

QED

Lemma 4: Gauss's Lemma for Quadratic Residues

If p is an odd prime and gcd(q,p)=1, then:


where:
μ = the number of elements in qP ∩ N
P = { 1, 2, ... (p-1)/2 }
N = { -1, -2, ... -(p-1)/2 }

(1) Let x,y be elements of P such that x ≠ y.

(2) qx is not congruent to ± qy (mod p) (from Lemma 2 above)

(3) So, we see from (2) that there are (p-1)/2 distinct congruence classes that are created from qP since for each combination, we know from (2), that there is no overlap.

(4) q(p-1)/2 ≡ (∏εi) (mod p) where εi = 1 if (i) ∈ P and εi = -1 if (i) ∈ N [From Lemma 3 above]

(5) So, q(p-1)/2 ≡ (-1)μ (mod p) where μ = the number of elements in qP ∩ N since:

(a) (∏εi) = (-1)μ where μ is the number of times εi = -1. [Since we can ignore all the times εi = 1]

(b) But this means we need to figure out the count of all elements b ∈ qP that are also in N.

(c) And this means that we are looking for the number of elements in qP ∩ N.

(6) By Euler's Criterion (see here), we know that:


(7) Combining (5) and (6) gives us our conclusion since the Legendre symbol is only = to 1 or -1.


QED

Quadratic Reciprocity: The Proof

Today, I will present a proof for the Principle of Quadratic Reciprocity:


For those not familiar with quadratic reciprocity, quadratic residues, or with the notation above, start here.

Today's proof is based on the Gareth A. Jones and J. Mary Jones Elementary Number Theory.

Theorem 1: Principle of Quadratic Reciprocity.

Given p,q are odd primes. if p or q ≡ 1 (mod 4), then p is a quadratic residue of q if and only if q is a quadratic residue of p. if both p and q ≡ 3 (mod 4), then p is a quadratic residue of q if and only q is not a quadratic residue of p and likewise, q is a quadratic residue of p if and only if p is not a quadratic residue of q.

(1) Let P be the set of integers {1, 2, ... (p-1)/2 }

(2) Let N be the set of integers -P, that is, {-1, -2, ... -(p-1)/2}

(3) Let Q be the set of integers {1, 2, ... (q-1)/2 }

(4) Now by Gauss's Lemma (see here):


where μ is the number of elements in qP ∩ N. [See here for details on qP ∩ N]

(5) Further, we can conclude (see here):


where μ + ν is the number of pairs (x,y) ∈ PxQ such that -p/2 is less than qx-py is less than q/2.

(6) From a result, I will show later, there exist values α and β such that:

μ + ν = (p-1)(q-1)/4 - (α + β).

(7) Now, it can be shown (see Lemma 2 here), that α = β

(8) With this in place, we combine (#5) with (#6) to get (see Lemma 3 here):


QED

Note: if you are unclear how (#8) is equivalent to the given, see here.

Friday, January 27, 2006

Quadratic reciprocity

Today's blog will focus on the following concepts: quadratic residues, Legendre symbol, and quadratic reciprocity.

The proof for the Rule of Quadratic Reciprocity can be found here.

For details on how quadratic reciprocity relates to the history of Fermat's Last Theorem, see here.

1. Quadratic Residues

The set of quadratic residues is an important concept that derives from modular arithmetic. It is the set of possible congruence values for a given value x2. For example, let's look at the quadratic residues for mod 7.

There are 7 possible values for x (mod 7): 0, 1, 2, 3, 4, 5, 6 but we only need to consider the nonzero ones.

To figure out the quadratic residues, we look at the following values:

12 ≡ 1 (mod 7)
22 ≡ 4 (mod 7)
32 ≡ 9 ≡ 2 (mod 7)
42 ≡ 16 ≡ 2 (mod 7)
52 ≡ 25 ≡ 4 (mod 7)
62 ≡ 36 ≡ 1 (mod 7)

So we see that the quadratic residue for 7 consists of { 1, 2, 4}

For purposes of this blog, I will represent the quadratic residue of 7 as Q7 so that we have:

Q7 ≡ { 1, 2, 4 }

Since:

12 ≡ 1 (mod 5)
22 ≡ 2 (mod 5)
32 ≡ 4 (mod 5)
42 ≡ 1 (mod 5)

Q5 ≡ { 1, 2, 4 }

2. Legendre Symbol

The Legendre Symbol is a function that can be defined in terms of quadratic residues. Consider:


This value is defined to equal 0, 1, or -1. In the case above, p is an odd prime and a is any integer. The value is 0 if p divides a. The value is 1 if a is an element of Qp. The value is -1 if a is not an element of Qp

We know that Q7 ≡ { 1, 2, 4}.

If p = 7, a = 14, we know that the value of the Legendre Symbol is 0.

If p = 7, a = 15, we know that the value of the Legendre Symbol is 1 [since 15 ≡ 1 (mod 7)]

If p = 7, a = 17, we know that the value of the Legendre Symbol is -1 [ since 17 ≡ 3 (mod 7)]

3. Quadratic Reciprocity

The idea of quadratic reciprocity builds on top of the Legendre Symbol and refers to the relationship between two odd primes.

In a nutshell, the Rule of Quadratic Reciprocity states the following:


Reviewing exponents, it says that the multiple of two Legendre symbols of two primes is equal to -1 to the power of (p-1)*(q-1)/4. Since p,q are odd primes, p-1 and q-1 are even numbers and their product is divisible by 4.

There are two implications from this.

(1) If p or q ≡ 1 (mod 4), then:


That is, p is a quadratic residue modulo q if and only if q is a quadratic residue modulo p.

This is true since:

(4k+1-1)(4k+1-1)/4 = 16k2/4=4k2=2(2k2)

(4k+1-1)(4k+3-1)/4 = (4k)(4k+2)=(16k2 + 8k)/4=4k2+2k =2(2k2 + k)

and

(-1)2k' = 1.

(2) If both p and q ≡ 3 (mod 4), then:


That is, p is a quadratic residue modulo q if and only q is not a quadratic residue modulo p.

This is true since:

(4k+3-1)(4k+3-1)/4 =[16k2 + 16k + 4]/4 = 4(k2 + k) + 1.

and

(-1)4k' + 1 = -1.

This theorem is surprising and nontrivial. Carl Friedrich Gauss considered it one of the most beautiful theorems in all of number theory and worked through 7 different proofs of it. Leonhard Euler first conjectured the theory in 1783. Adrien Legendre provided several attempts at proofs. Still, it was Gauss in 1783 at the age of 18 who provided the first valid proof.

Overview of the background to Kummer's Proof

Ernst Kummer's proof for Fermat's Last Theorem was a major breakthrough in the history of number theory.

To appreciate the importance of Kummer's work with complex numbers, it is valuable to review earlier developments. Kummer came to his discoveries by trying to generalize quadratic reciprocity so it makes sense to review the details behind the basic proof for quadratic reciprocity. Lamé's work used cyclotomic integers which are derived from the roots of unity. For this reason, I will review basic proofs about π and Euler's famous equation: eiπ = -1.

Kummer's work became the foundation for algebraic number theory. From this view, it makes sense to follow up Kummer's proof with the work of Abel, Galois, as well as the transcendental nature of π.

With this background, it makes sense to go through Dedekind's reinterpretation of Kummer's work which became the foundation of modern algebraic number theory.

Ernst Eduard Kummer

Ernst Eduard Kummer was born in January 29, 1810 in Brandenburg, Prussia. His father was a physician who died when Ernst was 3 years old.

When he was 18, he entered the University of Halle with the intention of becoming a protestant minister. As part of his degree, he was required to take math classes. Over time, he switched his major from theology to mathematics.

In 1831, he won a prize for a mathematical essay that he had written. In honor of this essay, the university awarded him a doctorate in addition to his teaching certificate. That same year, he was teaching mathematics at the Gymnasium.

In 1832, he received a more permanent position at the Gymnasium in Leignitz. There he stayed for 10 years. While there, he taught mathematics and physics. One of his students at this time Leopold Kronecker became a very famous mathematician himself. During this time, Krummer also worked hard on mathematical research and wrote an important paper on hypergeometric series in 1836. From this paper, he began a correspondence with the mathematicians Carl Jacobi and Johann Dirichlet. In 1839, while he was still a school teacher, he was elected to the Berlin Academy of Science.

Life was picking up for Ernst Kummer. In 1840, he married a cousin of Dirichlet and in 1842, he became a full professor at the University of Breslau. Sadly, his wife died in 1848.

In 1855, Kummer became a professor of mathematics at the University of Berlin. He was also able to arrange for his colleagues Karl Weierstrass and Leopold Kronecker to also get positions at the University of Berlin. From this point, Berlin became one of the leading mathematical centers of all Europe.

Kummer made major contributions to function theory and number theory. In function theory he extended Gauss's work on hypergeometric series. In number theory, he proposed the concept of "ideal" numbers which later led to the theory of rings which is the foundation of modern algebraic number theory. His work on number theory also led to a major breakthrough on Fermat's Last Theorem.

For his work on Fermat's Last Theorem, Kummer won the Grand Prize from the Paris Academy of Sciences in 1857. He was later elected to the Paris Academy of Science and the Royal Society of London in 1863.

Kummer died on May 14, 1893 when he was 83.

References

Wednesday, January 25, 2006

Lamé's Proposed Proof

On March 1, 1847, Gabriel Lamé announced that he believed that he had found a full proof for Fermat's Last Theorem. He presented to the Paris Academy the outline of what he believed was a complete proof. Earlier he had succeeded in the first proof for x7 + y7 = z7.

The approach that he offered involved what are known as the Roots of Unity. This involves complex numbers such as α where:

αn = 1 and α ≠ ± 1.

The proof is based on the following equation:

xn + yn = (x + y)(x + αy)(x + α2y) .... (x + αn-1y)

The essence of the proof is showing that each of the x+αey is relatively prime to the others so that it represents an nth power (since they are all equal to zn). Then, one shows how this condition leads to infinite descent.

Lamé claimed that this work was largely based on the work done by Joseph Liouville.

Liouville was present at the Paris Academy at this time and spoke after Lamé. He was not as confident as Lamé about the success of the proof. In fact, he suggested that Lamé approach was rather obvious and would have occurred to anyone who had worked long enough with complex numbers.

Liouville claimed that Lamé's assumption about unique factorization of the roots of unity was not necessarily justified and absent unique factorization, the proof was not valid.

The next person to speak was Augustin Cauchy. Cauchy was more optimistic about the possibilities of Lamé's approach. He announced that he too was very close to a solution to Fermat's Last Theorem using a similar technique.

On March 15, Pierre Wantzel announced that he had a proof about the unique factorization of the roots of unity. His proof showed unique factorization for the case where n = 2 and n=3. He then claimed that "one easily sees" the validity for cases where n ≥ 4. In a short time, Cauchy came back demonstrating that Wantzel's method did not work for n ≥ 4.

At this point, a competition broke out between Lamé and Cauchy to prove unique factorization for n ≥ 4. On March 22, both men deposited "secret packets" to the Paris Academy, a method that was used to establish priority.

Unfortunately, as is usually the case, the devil is in the details and the proof for unique factorization turned out to be more complicated than Lamé and Cauchy had forseen. In May 24, Liouville announced a proof by Ernst Kummer that settled the question by demonstrating that Lamé's complex numbers lacked unique factorization. In fact, Kummer had first presented this proof in a mathematical journal three years earlier.

But there was hope. Kummer's conclusion was that unique factorization could be "saved" by using "ideal complex numbers." Kummer's ideal complex numbers would turn out to be a major breakthrough in the generalization of Fermat's Last Theorem. It would also turn out to be the foundation for what is today known as algebraic number theory.

Today's blog was taken from Harold M. Edwards' Fermat's Last Theorem: A Genetic Introduction to Algebraic Number Theory. (All quotes come from Edwards' original text).

Tuesday, January 24, 2006

So ends Phase I of the History of Fermat's Last Theorem

With yesterday's posting, I have completed Phase I of the history of Fermat's Last Theorem.

The original goal of this blog was to divide up the history into three phases:

Phase I: Early Achievements

Phase II: Kummer's Achievement

Phase III: Wile's Achievement

As part of the first phase, I have done blogs on the following mathematicians:
It was very fun to revisit the early proofs and I was very surprised at the response that I received. To date, this blog has been growing by 10-20% each month since April of last year. This month, this blog will have over 2500 unique visitors.

Thanks to everyone who has provided questions and comments on the different parts of each proof. Please continue to point out areas which are unclear or details which can be improved.

Thanks to everyone for your support. I am very glad (and surprised) to see that there is a growing audience for number theory and for a blog that is not much more than the details behind famous mathematical proofs.

Cheers,

-Larry

Monday, January 23, 2006

Fermat's Last Theorem: Proof for n=7: v cannot be even

In today's blog, I will continue the proof for Fermat's Last Theorem n=7.

The details for today are based on Paulo Ribenboim's Fermat's Last Theorem for Amateurs.

Lemma 1: if :
(a) 2 * 74e-1 *A4= s2 + 3 * 72ev2 ± u
(b) 2 * B4
= s2 + 3 * 72ev2 ± u
(c) s, A, B, v are an integers
(d) gcd(A,B) = 1
(e) v is even
(f) s is odd
Then
B is not even

Proof:

(1) Assume B is even

(2) Then A is odd

(3) Adding the two values together gives us:
( s2 + 3 * 72ev2 ± u) + ( s2 + 3 * 72ev2 ± u) = 2s2 + 2*3*72ev2 = 2 * 74e-1 *A4 + 2 * B4

(4) Dividing both sides by 2 gives us:
s2 + 3*72ev2 = 74e-1 * A4 + B4

(5) Subtracting 3*72ev2 from both sides gives us:
s2 = -3*72ev2 + 74e-1*A4 + B4

(6) But from #5 and from a previous result (see here), we get:
s2 ≡ (-3)(1)(v2) + (-1)4e-1(1) + (B2)2 (mod 8)

(7) Also, from a previous result (see here), we know that B2 ≡ 0 or 4 (mod 8).

(8) So that (B2)2 ≡ 0 (mod 8) since:

(a) (0)2 ≡ 0 (mod 8)

(b) (4)2 ≡ 16 ≡ 0 (mod 8)

(9) So applying (#9) to (#7) gives us:
s2 ≡ (-3)v2 + (-1)4e-1(1) + (0) ≡ (-3)v2 - 1.

(10) But since v is even, there exists v' such that v = 2v' and this means that:
v2 ≡ (2v')2 ≡ 4v'2 ≡ 0 since:

(a) So, v'2 ≡ 0 or 4 (mod 8)

(b) (4)(0) ≡ 0 (mod 8)

(c) (4)(4) ≡ 16 ≡ 0 (mod 8)

(11) Combining (#11) with (#10) gives us that:
s2 ≡ -1 (mod 8).

(12) But this is impossible since s2 ≡ 1 (mod 8) by a previous result (see here)

(13) So we have a contradiction and we reject our assumption.

QED

Lemma 2: if:
(a) 2 * 74e-1 *A4= s2 + 3 * 72ev2 ± u
(b) 2 * B4
= s2 + 3 * 72ev2 ± u
(c) s, A, B, v are an integers
(d) gcd(A,B) = 1
(e) v is even
(f) s is odd
(g) A is even
Then
There exists an integer A'' such that A = 8A''

Proof:

(1) B is odd [since A is even and gcd(A,B)=1]

(2) Since A is even, there exists a value A' such that A= 2A'

(3) Since s is odd and from a previous result (see here), we have:
s2 ≡ 1 (mod 8)

(4) Adding (a) and (b), we get:
2*s2 = -3 *2* 72ev2 + 2*74e-1A4 + 2*B4

(5) Since 2v=AB, we can also write:
s2 = -3 * 72e([1/2]AB)2 + 74e-1A4 + B4 =
= -3*72e(A'B)2 + 74e-1A4 + B4

(6) From (#5) and a previous result (see here):
s2 ≡ (-3)(1)(A')2(1) + (-1)4e-1(0) + (1) ≡
≡ (-3)(A')2 + 1 (mod 8)

(7) Combining (#6) with (#3) gives us:
s2 ≡ (-3)(A') + 1 ≡ 1 (mod 8)

(8) This implies:
(-3)(A')2 ≡ 0 (mod 8)

(9) Which mean that A' must be divisible by 4 since:

(-3)(0)2 ≡ 0 (mod 8)
(-3)(1)2 ≡ -3 (mod 8) which doesn't work.
(-3)(2)2 ≡ (-3)(4) ≡ -4 (mod 8) which doesn't work
(-3)(3)2 ≡ (-3)(9) ≡ -27 ≡ -3 (mod 8) which doesn't work
(-3)(4)2 ≡ (-3)(16) ≡ -48 ≡ 0 (mod 8)
(-3)(5)2 ≡ (-3)(25) ≡ -75 ≡ -3 (mod 8) which doesn't work
(-3)(6)2 ≡ (-3)(36) ≡ -108 ≡ -4 (mod 8) which doesn't work
(-3)(7)2 ≡ (-3)(49) ≡ -147 ≡ -3 (mod 8) which doesn't work

(10) So there exists A'' such that A' = 4A'' = 8A

QED

Lemma 3: if :
(a) 2 * 74e-1 *A4= s2 + 3 * 72ev2 ± u
(b) 2 * B4
= s2 + 3 * 72ev2 ± u
(c) s, A, B, v are an integers
(d) gcd(A,B) = 1
(e) v is even
(f) s is odd
(g) A is even
Then
There exists A'' such that A=8A'' and:
(s - B2 + 3*8*72eA''2)(s + B2 - 3*8*72eA''2) = 74e-1*4*(2A'')4

Proof:

(1) From Lemma 2 above, we know that there exists A'' such that A=8A''.

(2) Adding (a) and (b) together gives us:
s2 = -3 * 72e([1/2]AB)2 + 74e-1A4 + B4 =
= -3*72e(A'B)2 + 74e-1A4 + B4

(3) -3*16*72e(A'')2B2 + 74e-1*84*(A'')4 + B4

(4) Now,
(B2 - 3*8*72e(A'')2)2 = B4 - 2*3*8*72e(A'')2B2 + 9*64*74e(A'')4

(5) So,
s2 - (B2 - 3*8*72e(A'')2)2 = 74e-1*84*(A'')4 - 32*82*74e(A'')4 =
= 74e-1(84*(A'')4 - 32*82*7(A'')4) =
= 74e-1*82(82(A'')4 - 32*7(A'')2) =
= 74e-1*82(64(A'')4 - 63(A'')4) =
= 74e-1*82(A'')4

(6) Putting it altogether gives us:
(S - B2 + 3*8*72e(A'')2)(S + B2 + 3*8*72e(A'')2) = 74e-1*82*(A'')4 =
= 74e-1*4*(2A'')4

QED

Lemma 4: x2 ≡ 0, 1, 2, or 4 (mod 7)

Proof:

(0)2 ≡ 0 (mod 7)
(1)2 ≡ 1 (mod 7)
(2)2 ≡ 4 (mod 7)
(3)2 ≡ 9 ≡ 2 (mod 7)
(4)2 ≡ 16 ≡ 2 (mod 7)
(5)2 ≡ 25 ≡ 4 (mod 7)
(6)2 ≡ 36 ≡ 1 (mod 7)

QED

Lemma 5: if :
(a) 2 * 74e-1 *A4= s2 + 3 * 72ev2 ± u
(b) 2 * B4
= s2 + 3 * 72ev2 ± u
(c) s, A, B, v are an integers
(d) gcd(A,B) = 1
(e) v is even
(f) s is odd
(g) A is even
Then
There exists A'' such that A=8A'' and:
(s - B2 + 3*8*72eA''2)(s + B2 - 3*8*72eA''2) ≠ 74e-1*4*(2A'')4

Proof:

(1) Assume that (s - B2 + 3*8*72eA''2)(s + B2 - 3*8*72eA''2) = 74e-1*4*(2A'')4.

(2) Both (s - B2 + 3*8*72eA''2) and (s + B2 + 3*8*72eA''2) are even since:

(a) s is odd, B is odd (since A is even and gcd(A,B)=1.)

(b) odd - odd + even = even

(c) odd + odd + even = even

(3) gcd(s - B2 + 3*8*72eA''2 , s + B2 - 3*8*72eA''2) = 2 since:

(a) Let p be a prime that divides both and which does not equal 2.

(b) Since p divides both it also divides (s - B2 + 3*8*72eA''2 ) + (s + B2 + 3*8*72eA''2) = 2s.

(c) Since p is odd, it divides s.

(d) By assumption p must divide 74e-1*4*(2A'')4.

(e) But this means p must divide 74e-1 or A''.

(f) p ≠ 7 since it divides s and s is not divisible by 7.

(g) p cannot divide A'' since by S - B2 + 3*8*72eA''2, it would have to divide B but this is impossible since gcd(A,B)=1.

(h) So we have a contradiction and decide that p=2.

(i) Let f be the gcd. By (h), it must be a power of 2.

(j) By the logic in (b), it must divide 2s which means that it must = 2 since s is odd.

(4) From (#1), we can conclude that:

(a) 74e-1 divides 1 of the two multiples.

(b) We know that there exists c,d such that cd=2A'' and c4 divides 1 of the multiplies and d4 divides the other and gcd(c4,d4) = 1.

(c) So, we can assume that:
s ± B2 ± 3*8*72eA''2 = 2c4

s ± B2 ± 3*8*72eA''2 = 74e-12d4

(5) Subtracting these two equations so that we remove the s gives us:
± 2B2 = ±6*8*72eA''2 - 2c4 + 74e-12d4

(6) Dividing both sides by 2 gives us:
± B2 = ± 6*4*72eA''2 - c4 + 74e-1d4 =
= ± 6*72e(2A'')2 - c4 + 74e-1d4 =
= ± 6*72ec2d2 - c4 + 74e-1d4

(7) We know that 7 does not divide B

If 7 divided B, then 7 would divide c from (#6), and then it would divide s from (#4c) which is impossible since s is not divisible by 7.

(8) And we also know that 7 does not divide c.

If 7 divided c, then 7 would divide B from (#6) and the same argument applies.

(9) So ± B2 + c4 ≡ 0 (mod 7) from (#6)

(10) But then we have ± B2 + (1, 2, or 4) which means ± must actually be "-".

(11) This then gives us: -B2 = -6*72ec2d2 -c4 + 74e-1d4

(12) Multiplying -1 to each side gives us:
B2 = c2 + 6*72ec2d2 - 74e-1d4

(13) But this equation leads to an infinite descent by a previous lemma (see step #5 in Lemma 1 here) since:

v = AB/2 = 4A''B ≥ 2cd which is greater than d.

(14) So we reject our assumption at (1).

QED

Lemma 6: If there exists s,u,v such that:
(a) (s2 + 3 * 72ev2 + u)(s2 + 3 *72ev - u) = 64 * 74e-1v4
(b) gcd(s2 + 3 * 72ev2 + u , s2 + 3 *72ev - u) = 2n where n ≥ 0.
(c) 7 doesn't divide s
(d) t = 7ev
(e) gcd(t,s)=1
Then
v is not even.

Proof:

(1) Assume that v is even.

(2) Then t must be even and s must be odd from (d) and (e).

(3) u must also be odd since:

(a) Assume u is even.

(b) (s2 + 3 * 72ev2 + u)(s2 + 3 *72ev - u) = 64 * 74e-1v4

(c) (odd2 + odd*odd*even + even)(odd2 + odd*odd*even - even) =
(odd + even + even)(odd + even - even) = (odd)(odd) = odd

(d) Which contradicts (b) so we reject our assumption (a).

(4) Since v is even, we know that there exists v' such that:
v = 2v'

(5) Since u is odd, we know that both (s2 + 3 * 72ev2 + u) and (s2 + 3 *72ev - u) are even since:

odd*odd + odd*odd*even*even + odd = odd + even + odd = even.

(6) This gives us the following:
(s2 + 3 * 72ev2 + u)(s2 + 3 *72ev - u) = (2)(2) * 74e-1(16)v4

(7) From (b) above we know that 74e-1 divides either one or the other since if it did not divide only 1, there would a common factor of 7 which is not the case.

(8) From (#6) and (#7), we can posit that there exists A,B such that:
AB = 2v

And (2v)4 = A4B4

(9) And putting this into (6) gives us:
(s2 + 3 * 72ev2 + u)(s2 + 3 *72ev - u) = (2)(2) * 74e-1(16)v4 = (2)(2)* 74e-1A4B4

Where:

2*74e-1A4 divides either (s2 + 3 * 72ev2 + u) or (s2 + 3 *72ev - u) and
2*B4 divides the other one.

(10) We note further that gcd( s2 + 3 * 72ev2 + u, s2 + 3 *72ev - u) can be at most 2 since:

(a) Let f = the greatest common denominator.

(b) f must divide (s2 + 3 * 72ev2 + u) - (s2 + 3 *72ev - u) = 2u

(c) We know from our assumption that f must be a power of 2.

(d) We also know that u is odd.

(e) This means that f must = 2.

(11) So, we have the following:

(a) s2 + 3 * 72ev2 ± u = 2 * 74e-1A4

(b) s2 + 3 * 72ev2 ± u = 2 * B4

(c) we can further conclude that gcd(A,B) = 1 since:

If an odd prime divides gcd(A,B), then this same odd prime would divide (s2 + 3 * 72ev2 + u) and (s2 + 3 *72ev - u) which goes against our assumption.

If 2 divides gcd(A,B), then then we would have 4 would divide both but this impossible since the gcd can be at most 2.

(d) There are two possible cases to consider:

(i) A is odd, B is even
(ii) A is even, B is odd

We know that they cannot both be even from (#11c). We know that one must be even since they are equal to 2v (#8)

(12) B is not even (see Lemma 1 above)

(13) So A is even.

(14) So (s - B2 + 3*8*72eA''2)(s + B2 - 3*8*72eA''2) = 74e-1*4*(2A'')4 [From Lemma 3 above]

(15) But simultaneously, from Lemma 5 above we have:
(s - B2 + 3*8*72eA''2)(s + B2 - 3*8*72eA''2) ≠ 74e-1*4*(2A'')4

(16) So we have a contradiction and we reject (#1).

QED